CVSS score on both flaws. Critical.
Contact and enquiry forms
No password needed. Just your contact form and an unpatched server. The leads in your inbox could be readable by anyone.
Your enquiry form could be the way in
Two critical flaws in PHP itself can let an attacker run code on your server without a login.
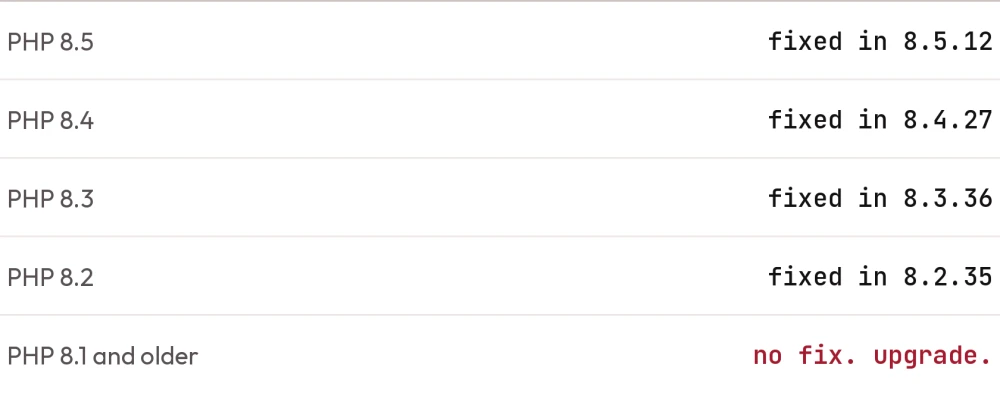
Every version from 5.4 to 8.5.11 is affected. On PHP 8.1 or older, no patch is coming.
9.2
CVSS score on both flaws. Critical.
0
Logins an attacker needs
5.48 - 5.11
PHP versions affected
PHP branch getting a fix
PHP2Shell sits in PHP itself, the language underneath WordPress, Drupal, Joomla, Laravel and Magento. Researchers showed it working against WordPress, Drupal and Joomla sites with no password at all.
That means no plugin update, theme update or security plugin closes it. The fix is a server-level PHP upgrade. And that's where most sites get stuck: plugins and themes written for PHP 7 often break on 8.2.
No password needed. Just your contact form and an unpatched server. The leads in your inbox could be readable by anyone.
Your enquiry form could be the way in
Old PHP, live checkout, open door. A shop on PHP 7 is a shop that can't be patched, and your customers paid by card.
Ecommerce and WooCommerce
Your homepage could be serving someone else's content by tomorrow. Hacked sites get flagged, and flagged sites lose their rankings.
SEO and reputation
We were on it whilst you were snoring. Our managed clients' servers were checked and patched before most people saw the headlines.
For sites on mass hosting where nobody can tell you which PHP you're on. We migrate the site, keep PHP patched at server level, monitor it and back it up. You don't get that with mass hosts.
For sites worth keeping. We clone your site to staging on PHP 8.2 or newer, find every plugin and theme that breaks, fix or replace them, then switch live with a rollback ready.
For sites stuck on PHP 5 or 7 because the build can't move. Sometimes rebuilding costs less than patching around a decade of shortcuts. We'll tell you honestly which it is.
An attacker could run code on your server, read data held in memory such as form submissions or customer details, inject spam or malware, or take the site down.
Not necessarily, as exploitation depends on how the server is set up. We can check for signs of compromise as part of the review.
Not necessarily, as exploitation depends on how the server is set up. We can check for signs of compromise as part of the review.
Only if you're on PHP 8.2 or newer. Hosts can patch supported versions, but they can't patch 8.1 or older because no fix exists. Many hosts still let sites run on PHP 7.4 to avoid breaking them.
It might, if you flip the switch on a live site. That's why we test on staging first, fix what breaks and only then go live, with a rollback ready.
The check is quick. The upgrade depends on how much needs fixing. We'll give you a timeline before you commit.
The PHP check is free. Any further work will be discussed and quoted for you.
The site is on PHP 5 or early 7 and heavily customised; rebuilding can cost less than patching around it. We’ll tell you honestly which applies.
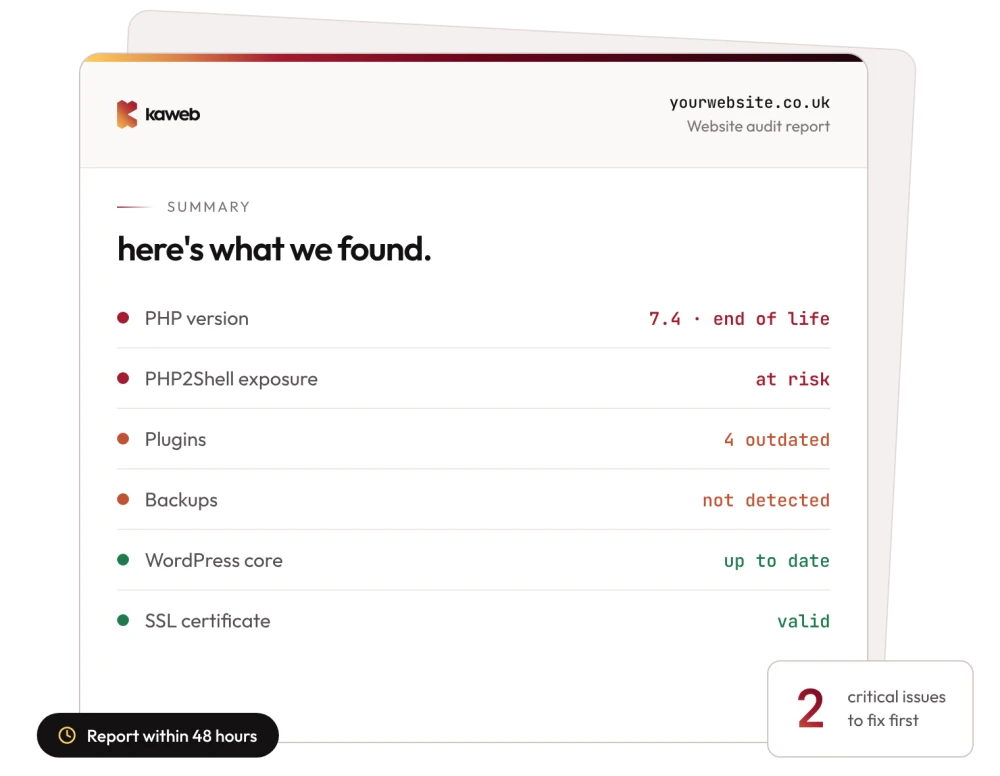
Free. Read-only. Report within 48 hours.
Request your free audit


